Introducing the new generation of LightKeeper PRO
The critical PHP2Shell vulnerabilities showed how fast attacks happen today. That's why we finished and are now releasing the new generation of LightKeeper PRO, a system for web hosting providers built around security.
On October 21, the PHP team released emergency fixes for two critical vulnerabilities named PHP2Shell (CVE-2026-109618 and CVE-2026-109619, severity 9.2 out of 10). Through them, an attacker could run their own code without logging in on any server where PHP serves websites. Exploitation attempts appeared even before the fixes were released.
Artificial intelligence helped find the vulnerabilities. Attackers have the same tools, so the time between a bug's disclosure and the first attacks is shrinking to hours. In the age of AI, hosting that nobody is watching is an easy target.
On our own hosting, we deployed the PHP fixes the same day, along with a web server rule that blocks the attack pattern. That experience settled it: we are releasing the new generation of LightKeeper PRO to other providers.
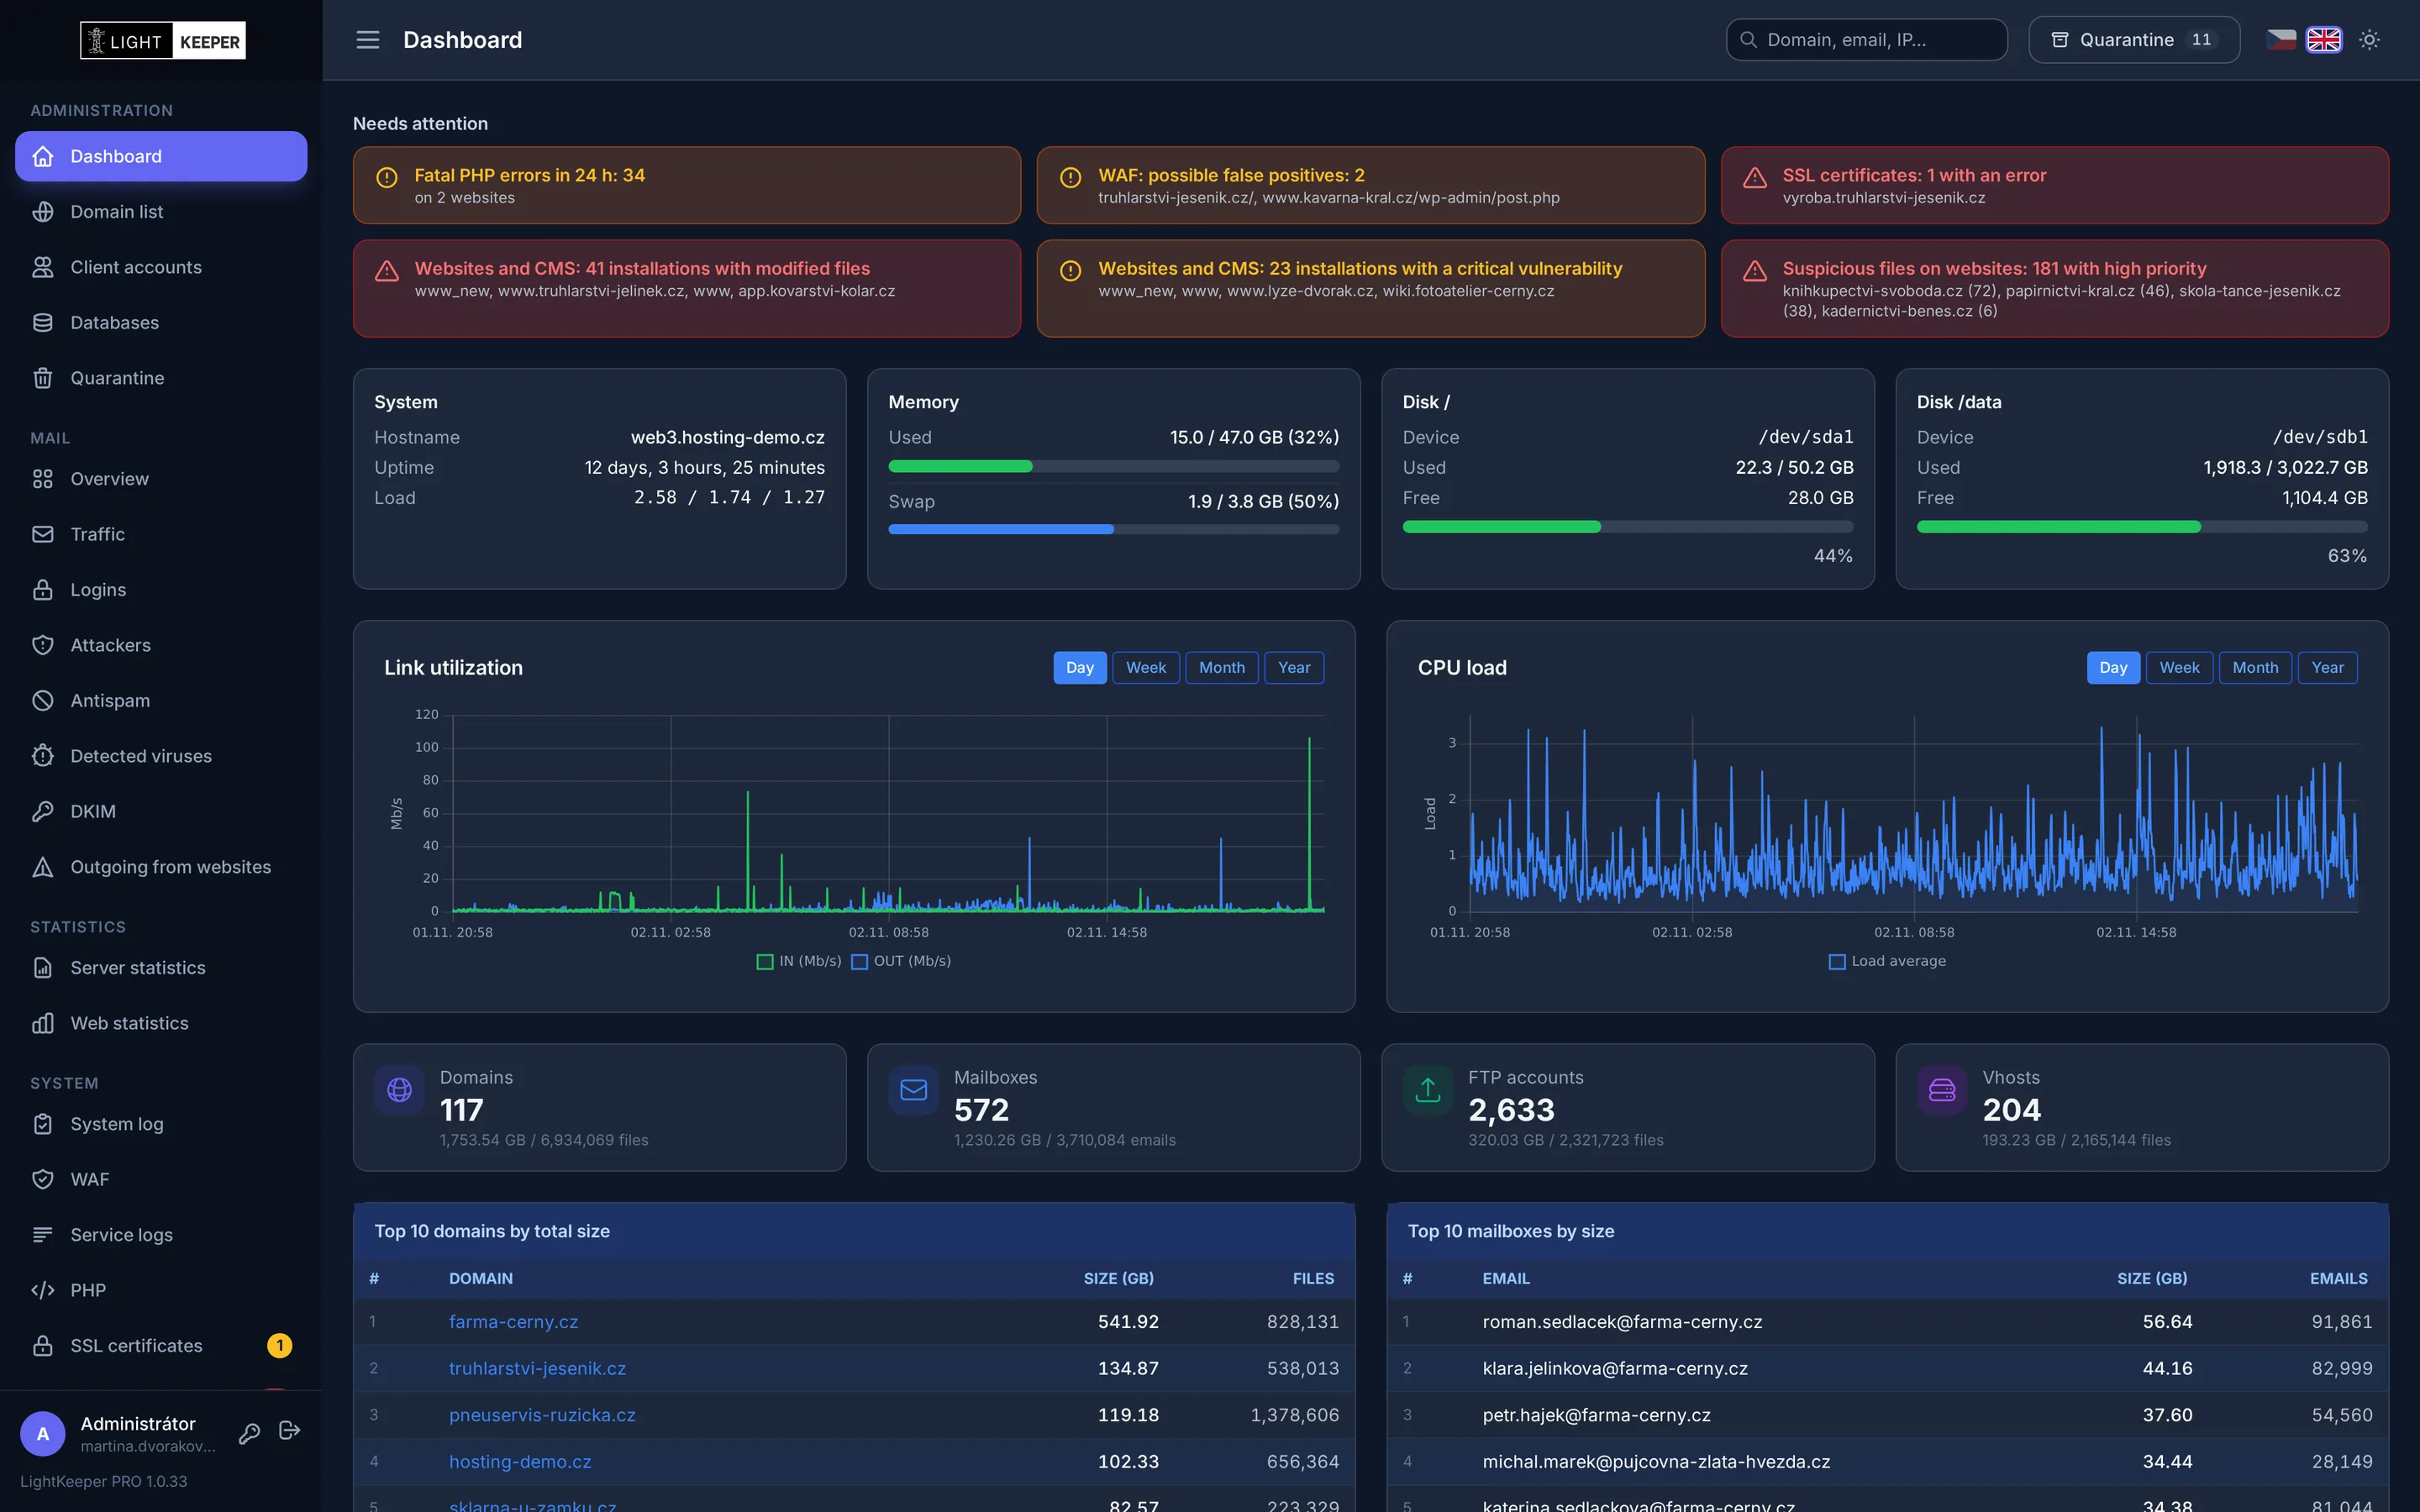
What the new generation brings
- Security of the whole solution: a web application firewall for all websites, an isolated PHP process for each website, protection for mail and mailboxes.
- Preventing problems: nightly scans for compromised WordPress and Joomla websites, daily certificate checks and alerts before the customer notices a problem.
- Detailed overview and statistics: attacks, spam, brute-force attempts, website traffic and server status in one place. Take a tour of the system.
Using the original LightKeeper PRO?
We'll deploy the new generation on your servers and migrate the data from the original LightKeeper into it. We recommend switching, because the original version has not been maintained for more than 10 years and receives no security fixes. Details in the FAQ.